 prawel.pl
JWT Decoder
Decode a JSON Web Token to read its header, payload claims, and expiry time in your browser. The token is never sent to a server.
Header
Payload
| Claim | Value | Date |
|---|
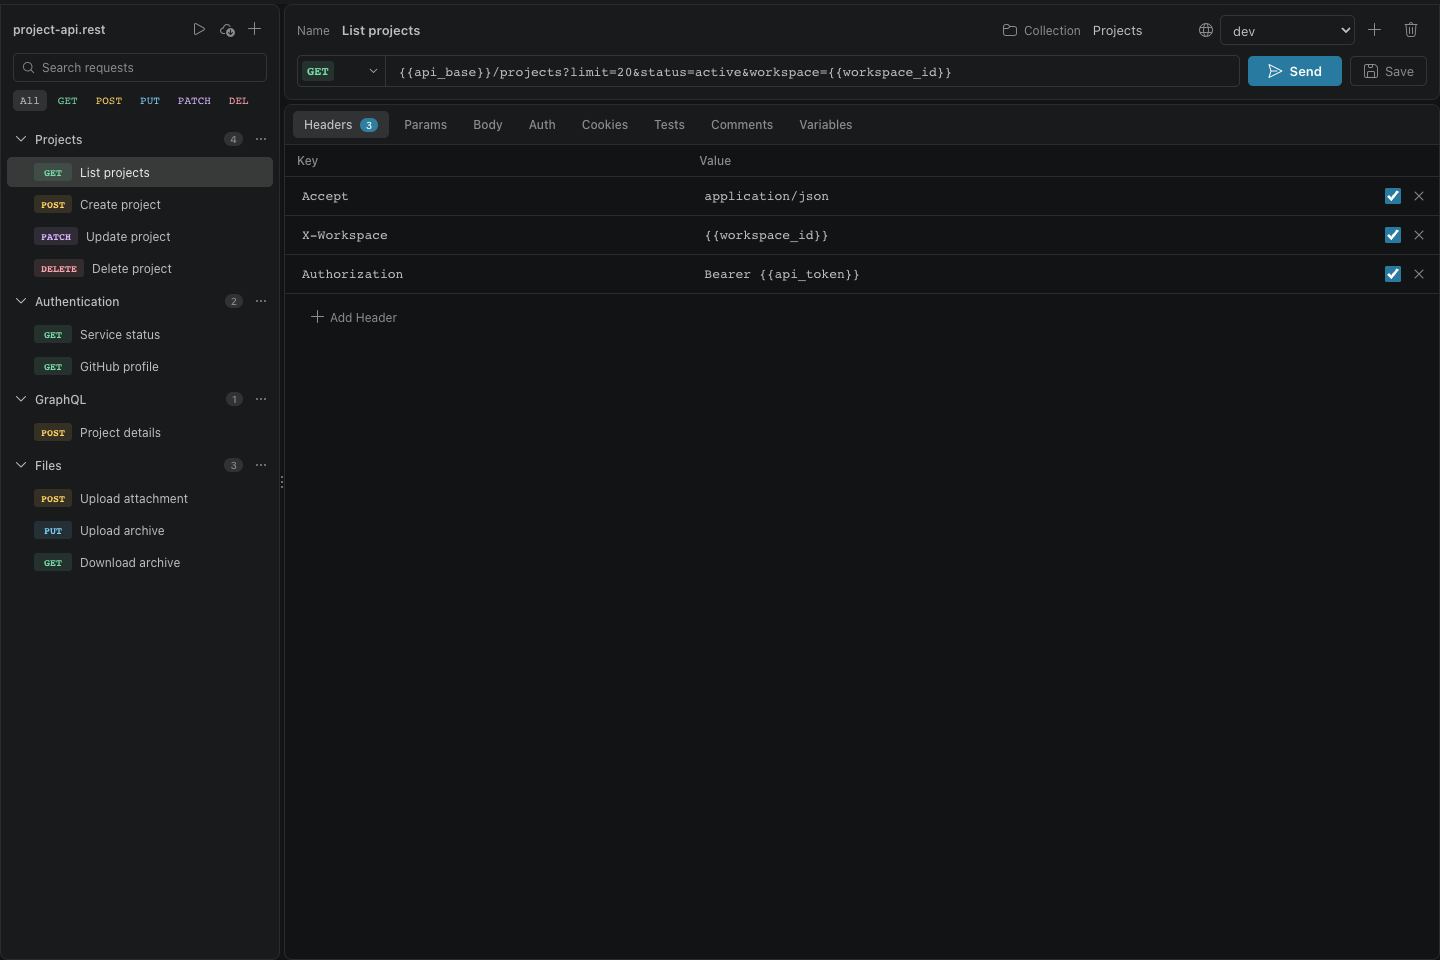
Visual REST Client
A graphical editor and secure, cookie-aware HTTP client for .rest and .http files, built directly into VS Code.
About this tool
A JWT has three Base64URL parts separated by dots: a header, a payload of claims, and a signature. This decoder shows the header and payload as formatted JSON and turns exp, iat, and nbf into readable dates.
Decoding does not verify the signature. Anyone can read a JWT, so never put secrets in its claims.
Runs entirely in your browser. Nothing you enter or open is uploaded.
Questions
- Is it safe to paste a production token?
- The token stays in this page. Treat it like a password anyway: anyone holding a valid token can call the API until it expires.
- Why does it say the token is expired?
- The exp claim is a Unix time in seconds. When it is earlier than your device clock, APIs reject the token.