 prawel.pl
PKCE Code Verifier and Challenge Generator
Generate an OAuth 2.0 PKCE code verifier and its S256 code challenge in your browser, and check a challenge against a verifier.
Authorization request parameters
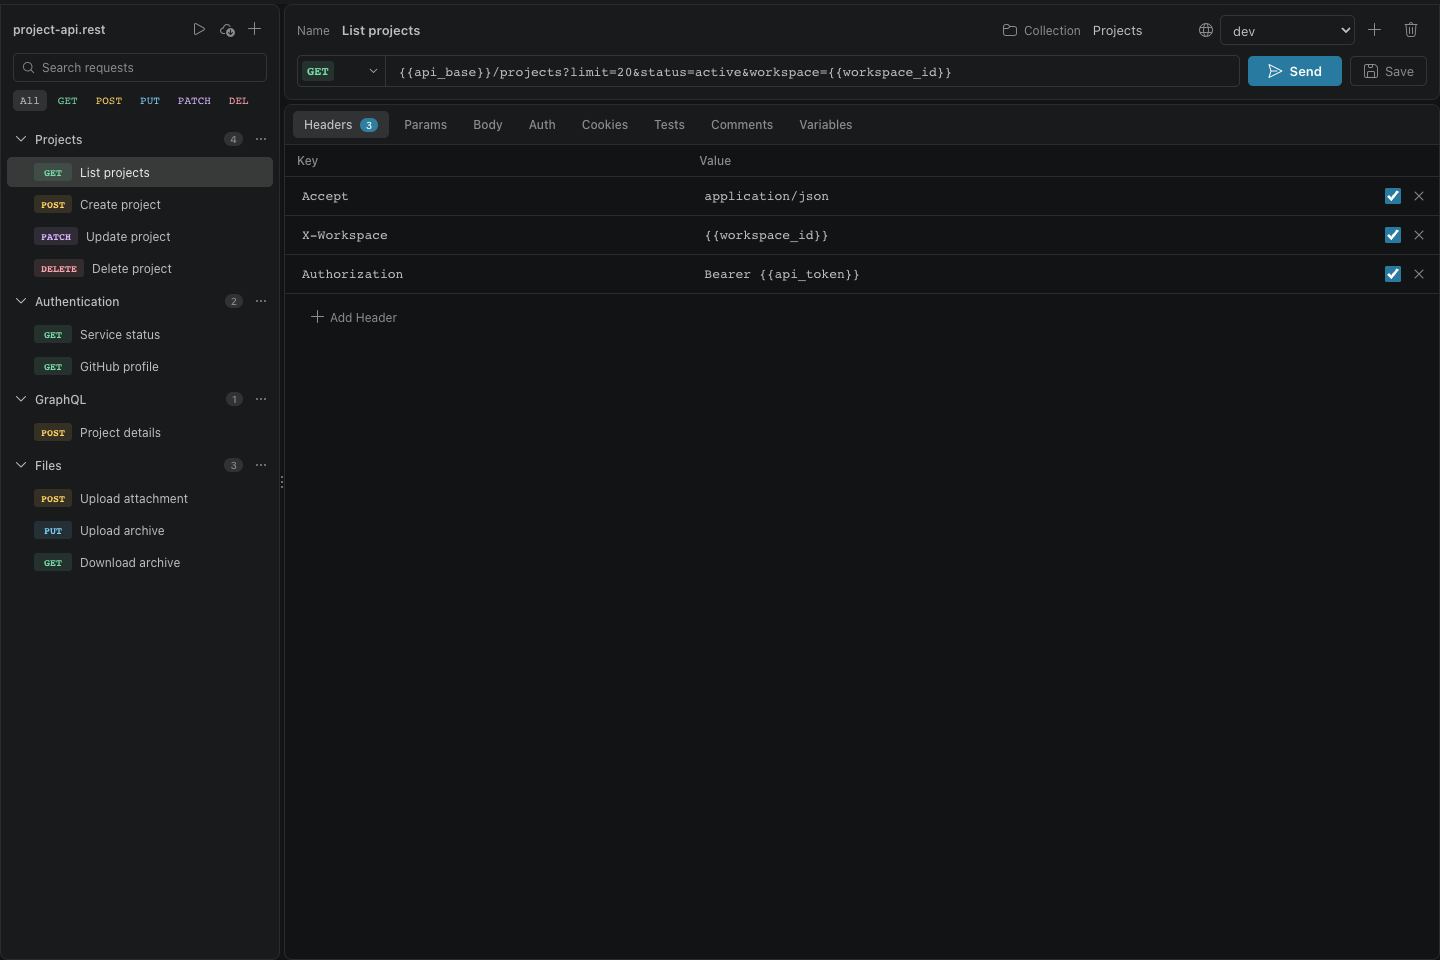
Visual REST Client
A graphical editor and secure, cookie-aware HTTP client for .rest and .http files, built directly into VS Code.
About this tool
PKCE (RFC 7636) protects the OAuth authorization code flow. The app sends a code challenge with the authorization request and proves it holds the matching code verifier when it exchanges the code for tokens.
The verifier is 43 to 128 random characters. The S256 challenge is the Base64URL-encoded SHA-256 hash of the verifier. Everything is computed with the Web Crypto API on your device.
Runs entirely in your browser. Nothing you enter or open is uploaded.
Questions
- Should I use plain or S256?
- S256. The plain method sends the verifier itself and is only allowed when a client cannot compute SHA-256.
- Can I reuse a verifier?
- No. Generate a new verifier for every authorization request.